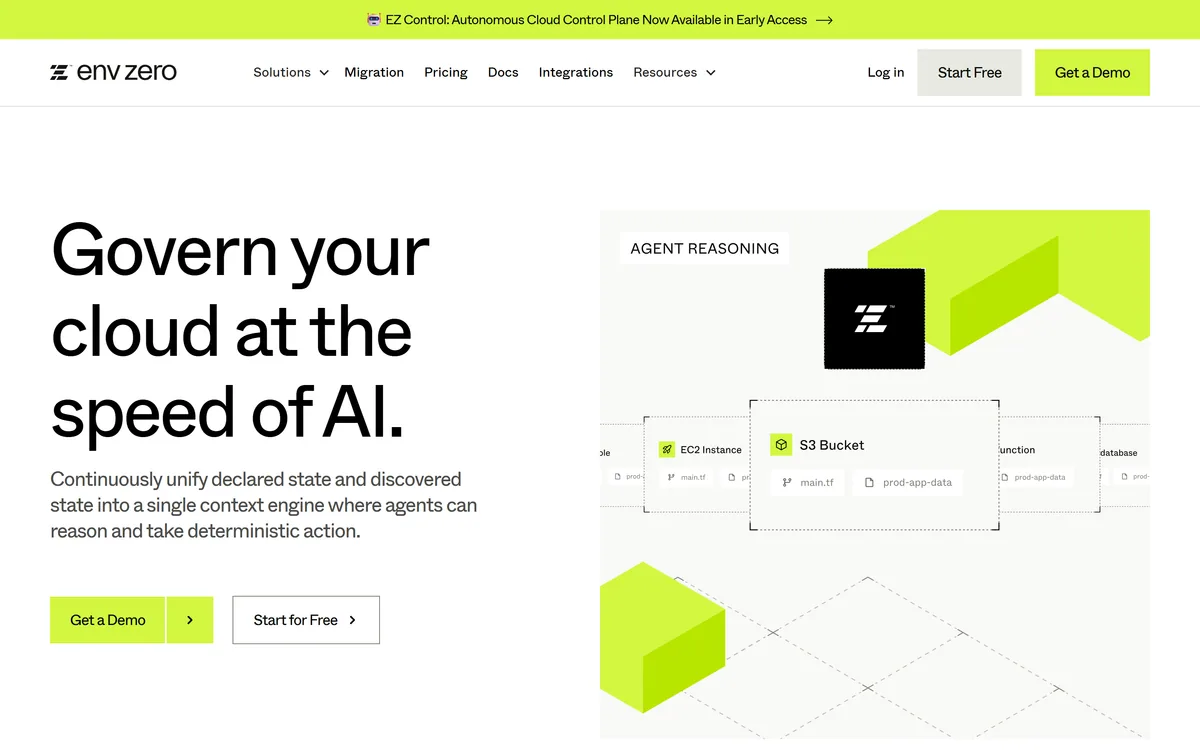
AI now writes infrastructure code faster than humans can review it, which is exactly where things drift, misconfigure and quietly diverge from policy. env0's pitch is to put governance around that speed so teams can deploy quickly without losing control.
It is an infrastructure-as-code management platform at heart: self-service templates with guardrails, drift detection and remediation, cloud asset management and continuous policy enforcement, with a newer control plane that unifies declared and discovered cloud state. It lives in the operations world alongside reliability tools like NeuBird, though its focus is provisioning governance rather than incident response.
This review covers what env0 puts around your infrastructure, where it earns its keep, how it is priced, and who it is oversized for.
env0, The Governance Brief
- env0 is an IaC management and governance platform: it automates Terraform and other infrastructure-as-code with guardrails.
- Governance is the core: self-service templates, RBAC, scoped variables and policy-as-code keep fast deployment safe.
- It keeps code and cloud in sync: drift detection and remediation, plus cloud asset management, address state that stops matching reality.
- The AI-era control plane is newer: an autonomous control plane is being rolled out; treat early-access pieces as evolving, not finished.
env0 Control-Plane Facts
| What it is | An IaC management and governance platform |
|---|
| Core | Automate Terraform and other IaC with guardrails |
|---|
| Self-service | Reusable templates, RBAC, scoped variables |
|---|
| Policy | Policy-as-code and continuous enforcement |
|---|
| Drift | Drift detection and remediation |
|---|
| Assets | Cloud asset management across environments |
|---|
| Connect | GitHub, GitLab or Bitbucket, no code changes |
|---|
| Newer | An AI-era control plane (parts in early access) |
|---|
Governing Cloud Infrastructure At The Speed Of AI
env0's core problem is a real one: infrastructure is now generated and changed faster than human review can keep up, so policies fragment, drift creeps in, and what is in your code stops matching what is in your cloud. env0 exists to close that gap by making fast deployment governed by default.
The way it does this is to sit between your IaC and your cloud, enforcing guardrails as infrastructure is provisioned rather than catching problems after the fact. That shift, from review-after to guardrails-during, is the substance behind the marketing language.
It is worth separating the established product from the newer ambition. env0 has a mature track record automating and governing Terraform and other IaC; its 'autonomous cloud control plane for the AI era', including an EZ Control capability, is a newer direction with parts in early access, which should be judged as evolving rather than finished.
So the fair framing is that env0 is a solid, established IaC governance platform that is extending toward AI-era autonomy. The core automation and guardrails are the dependable part; the autonomous control plane is the forward-looking part to evaluate on its own merits.
env0's shift, from review-after to guardrails-during, is the substance behind the language about governing at the speed of AI.
What Does env0 Put Around Your Infrastructure?
The platform is a set of governance capabilities layered over your existing IaC and version control.
Self-Service Templates And Policy-As-Code Guardrails
env0 lets developers and agents deploy infrastructure from reusable templates with Git-based workflows, while built-in guardrails, RBAC, scoped variables and policy-as-code keep that self-service safe. You connect existing code from GitHub, GitLab or Bitbucket without changing it, which lowers the barrier to adopting the governance layer.
The point is to empower fast deployment without handing out unchecked access. A reliability agent like Cleric watches production behaviour after release; env0 governs the provisioning step before it, so the two address different stages of keeping systems healthy.
Drift Detection, Asset Management And Audit
env0 continuously checks for drift between your declared state and your actual cloud, flags it and supports remediation, and provides cloud asset management so teams can see and control what is actually running. Continuous policy enforcement applies rules uniformly rather than leaving each team to interpret them.
Keeping declared and discovered state in agreement is the quiet, important job here, because unnoticed drift is how risk compounds. A root-cause tool like Resolve AI helps when something has already broken; env0 is upstream of that, trying to stop infrastructure diverging from policy in the first place.
Where env0 Earns Its Keep In Cloud Ops
env0 earns its keep for platform and cloud teams managing meaningful infrastructure-as-code who need to give developers self-service without losing governance, and who are feeling the gap between fast, AI-assisted change and slow human review.
It suits organisations with multiple teams and clouds where policies tend to fragment, because central templates, RBAC and policy-as-code bring consistency, and teams who are repeatedly bitten by drift between code and cloud.
It earns it less for a small team with a handful of resources managed by hand or a simple pipeline, where a dedicated governance control plane is more than the problem requires. Its case-study names are vendor-presented references, not a guarantee your environment will see the same results.
env0 offers a way to start for free and is sold with plans and demos aimed at platform teams and enterprises. We do not publish prices, which change; check the site.
The value question is whether the drift, misconfiguration and policy-fragmentation risk it removes outweighs its cost for your scale, which is an easy case for a large multi-team cloud estate and a weaker one for a simple setup.
Because you can connect existing code without changing it and start free, the sensible approach is to point env0 at a real repository, see how its guardrails and drift detection behave against your actual infrastructure, and judge the governance value before committing.
A Direct Way To Trial env0
Because its value is governance over real infrastructure, trial env0 against an actual repo and cloud, not a sample.
- Connect a real IaC repository from GitHub, GitLab or Bitbucket without changing the code.
- Deploy an environment from a template and confirm the Git-based workflow fits your team.
- Set RBAC, scoped variables and a policy-as-code rule, and test that the guardrails hold.
- Introduce a deliberate drift and check detection and remediation catch it.
- Review cloud asset management against what you believe is actually running.
- Pass/fail: env0 is worth it if its guardrails and drift control remove real risk at your scale.
- Evaluate any early-access autonomous features separately from the mature governance core.
env0 Infrastructure Terms
- Infrastructure as code (IaC)
- Defining cloud infrastructure in code (such as Terraform) so it can be versioned, reviewed and deployed repeatably rather than configured by hand.
- Policy as code
- Writing governance rules as code so they are enforced automatically and consistently during deployment, not applied manually afterwards.
- Drift
- When the real state of your cloud diverges from what your code declares, through manual changes or failures, creating hidden risk.
- Control plane
- The governing layer that sits between your IaC and your cloud, applying guardrails and keeping declared and discovered state in agreement.