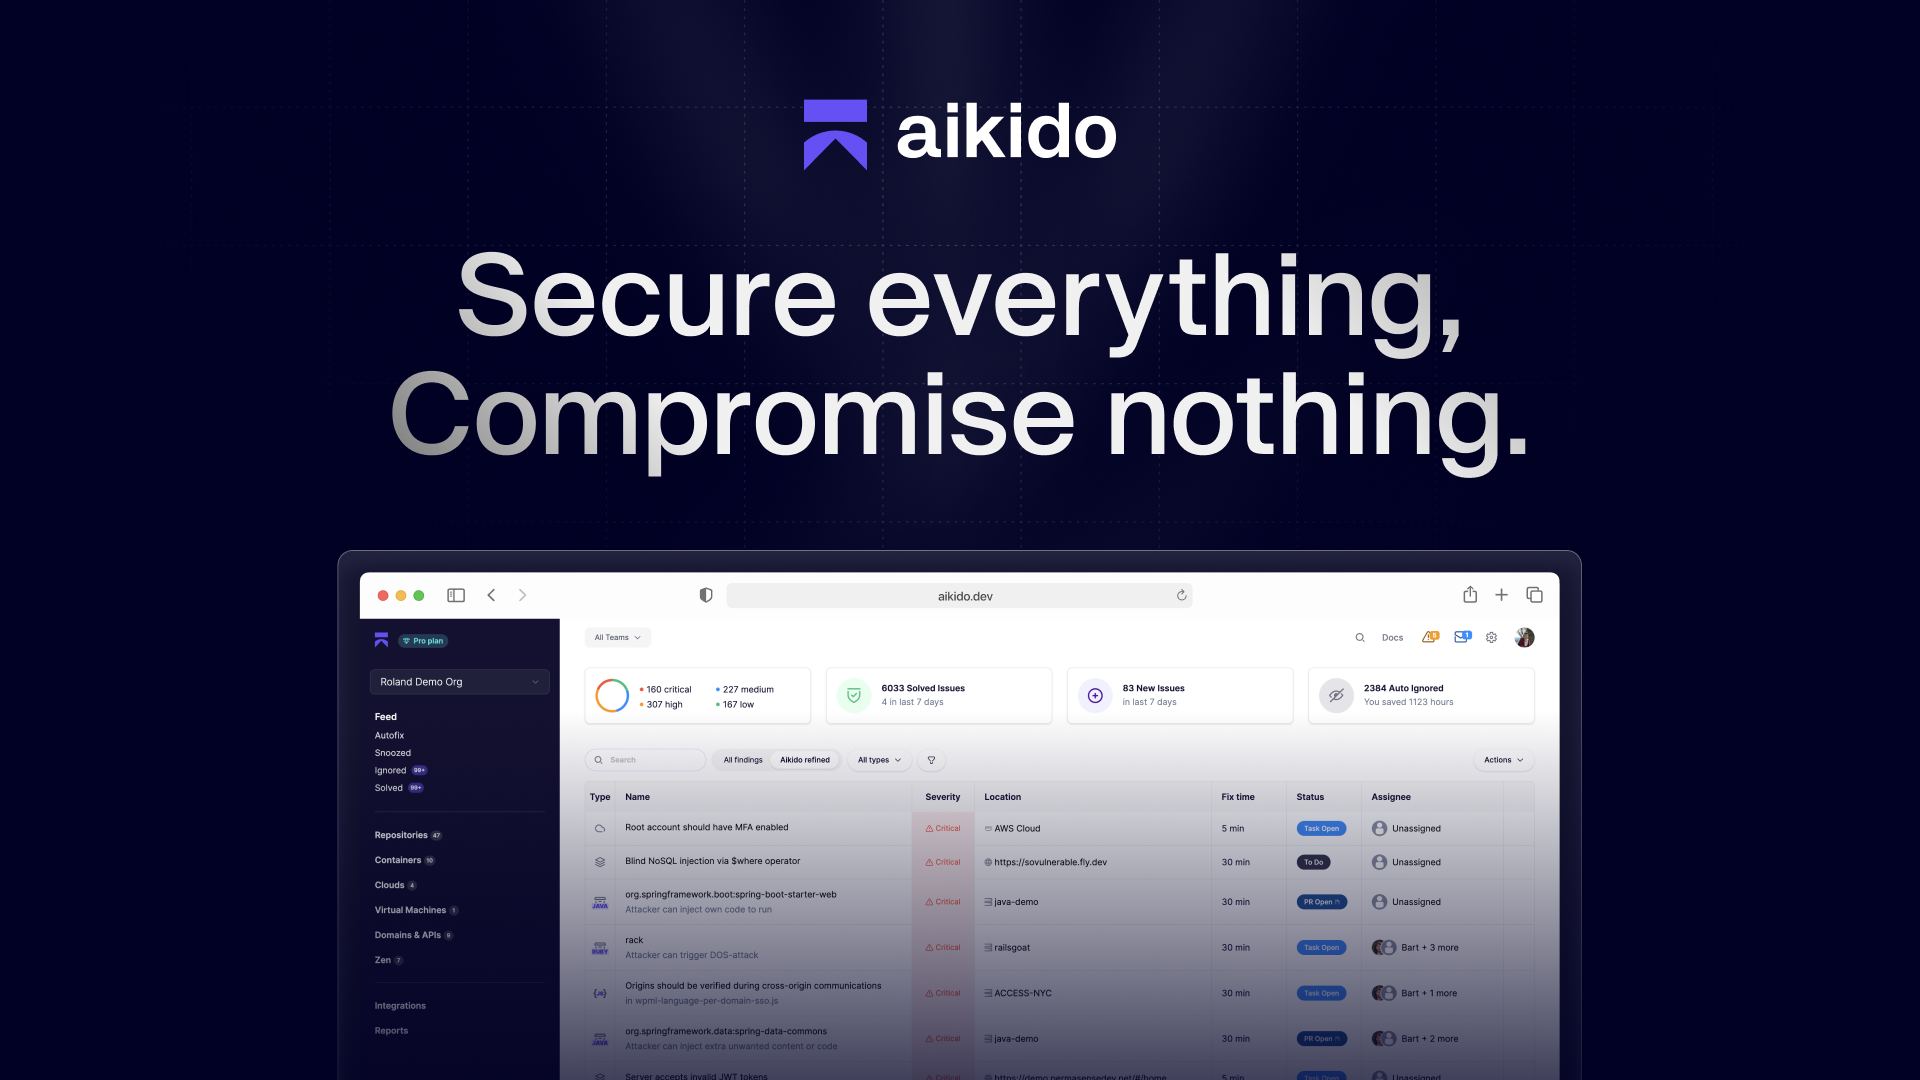
Aikido Security is a freemium product (free tier plus paid upgrades) listed on AInexfinder for people who need developer-first AI security from code to runtime. If you are searching for a Aikido Security review, what Aikido Security is, or how Aikido Security works in real projects, this page explains the product in plain language using the details on its listing — without restating the feature cards and pros/cons blocks that already appear on this page.
Developer-first AI security from code to runtime Category: Coding & Development. In short, Aikido Security is aimed at getting you from a clear task to a usable result with less manual busywork.
Searchers comparing Aikido Security alternatives usually want three answers: what the tool is for, whether the workflow matches theirs, and what trade-offs show up after the first week. This Aikido Security review is written for that decision — not as a sales page, and not as a copy of the bullet lists further down the page.
How Aikido Security works
At a high level, Aikido Security is built around a simple loop: you bring a clear input (a brief, a file, a prompt, or a task), you guide the process with the controls the product exposes, and you take away a draft or result you can refine. The exact input depends on the job — for example unified SAST, SCA, IaC, secrets, and cloud scanning — but the evaluation method stays the same: run one real task end-to-end and see if the output is usable.
In practice, people often start with unified SAST, SCA, IaC, secrets, and cloud scanning, then shape the output until it matches the job. Another part of the loop is AI AutoFix with automated remediation pull requests, which keeps the work moving without rebuilding the process from scratch each time.
Aikido Security also surfaces AI-driven noise reduction and prioritization, so teams can keep quality consistent across runs. When the task is more complex, IDE, CI, and repository integrations becomes the control that separates a rough draft from something you can actually ship.
Because Aikido Security is a freemium product (free tier plus paid upgrades), your first session should also test whether free limits (if any) or plan boundaries affect the task you care about. The listing describes the commercial model; this review focuses on how the work feels once you are inside the product.
Where Aikido Security fits in a workflow
Aikido Security is most useful when it plugs into a step you already do repeatedly: drafting, generating, editing, analyzing, automating, or preparing assets for a team. If your process is one-off and highly custom, a general-purpose assistant might be enough. If you keep returning to the same job, a focused product like Aikido Security can reduce setup time and keep results more consistent.
On this listing, the intended audiences include themes such as teams that need unified SAST, SCA, IaC, secrets, and cloud scanning, users who need AI AutoFix with automated remediation pull requests, teams that need AI-driven noise reduction and prioritization, and teams that need IDE, CI, and repository integrations. Treat those as starting hypotheses: the right test is whether Aikido Security shortens your real cycle time on a task you will repeat next week.
A practical pattern: pick one “golden path” task, write down the input you will use, define what “good enough” looks like, and run Aikido Security against that bar. That single experiment beats scanning feature names. If Aikido Security clears the bar with less rework than your current stack, it earns a longer trial.
What Aikido Security handles well
The strengths below are framed as outcomes, not a second feature list. The Key features and Pros cards on this page already inventory the listing facts; here the goal is to explain what those facts mean when you are mid-project.
Day to day, it helps that broad security coverage in one platform. Reviewers often notice that AI reduces false positives significantly.
A practical upside is that transparent flat-fee pricing with a free tier. For many teams, the value shows up because unified SAST, SCA, IaC, secrets, and cloud scanning.
On the capability side, unified SAST, SCA, IaC, secrets, and cloud scanning is one of the reasons people shortlist Aikido Security instead of a generic alternative. On the capability side, AI AutoFix with automated remediation pull requests is one of the reasons people shortlist Aikido Security instead of a generic alternative.
On the capability side, AI-driven noise reduction and prioritization is one of the reasons people shortlist Aikido Security instead of a generic alternative.
For SEO-minded readers evaluating “is Aikido Security any good,” quality usually means consistency under your constraints: speed, control, export format, and how much cleanup you still do. Run the same task twice. If Aikido Security stays stable and the edits you make are small, that is a stronger signal than a polished marketing page.
Limits and trade-offs with Aikido Security
No serious Aikido Security review should skip limits. The Cons card on this page captures listing trade-offs; the notes here explain how those trade-offs show up while you work, without dramatic language.
Before you commit, remember that best value requires connecting all repos and cloud accounts. Like most focused tools, Aikido Security is not perfect: higher tiers can be costly for large teams.
It is fair to note that team collaboration tools depend on your plan. A realistic trade-off is that customization options can take time to master.
Also plan for the usual AI-tool realities: edge cases need judgment, templates can feel generic until you add your own examples, and team rollout goes smoother when one person owns the first playbook. Aikido Security is strongest when you treat it as leverage on a defined job, not as a replacement for domain expertise.
Getting started with Aikido Security
A clean first hour with Aikido Security looks like this: open the product with one real task, ignore optional settings until you have a first draft, then tighten controls only where quality slips. Save a before/after note so you can compare against your previous process. That note becomes your internal “should we keep Aikido Security?” evidence.
On day one, focus on unified SAST, SCA, IaC, secrets, and cloud scanning and AI AutoFix with automated remediation pull requests. Those are enough to see whether the workflow matches your muscle memory. On day two, explore secondary controls only if the first path already saves time.
If Aikido Security is a freemium product (free tier plus paid upgrades), map your expected monthly volume in the first week. Limits, credits, or plan gates matter more after the novelty fades. Keep the evaluation tied to throughput you actually need.
Is Aikido Security a good fit for your team?
Aikido Security is a better fit when you have a recurring job aligned with developer-first AI security from code to runtime, when you can define quality in concrete terms, and when someone will own the rollout for a few weeks. It is a weaker fit when your needs change every day, when you need deep custom development the listing does not describe, or when you expected an all-in-one suite rather than a focused tool.
A balanced way to decide: if the upside around “Broad security coverage in one platform” outweighs the friction around “Best value requires connecting all repos and cloud accounts” on your actual task, keep testing. If the friction shows up every run, shortlist an alternative and compare side by side on the same input.
For buyers searching “Aikido Security vs alternatives,” insist on identical prompts or source files. Directory pages like this one help you shortlist; a controlled bake-off tells you what to buy.
Notes for evaluating Aikido Security
When you document a Aikido Security trial for stakeholders, capture: the task, the input, the settings you used, the time spent, the edits required, and whether a teammate could repeat the result without you. Those notes turn a vague “it felt good” demo into a decision other people can trust.
Also separate product quality from category hype. Aikido Security should be judged on the job listed for this page — developer-first AI security from code to runtime — not on whether it claims to do everything. Focused tools often win on reliability precisely because they refuse to be a Swiss army knife.
Finally, re-check this AInexfinder listing after your trial: features, pros, cons, and editor notes can help you brief a teammate, while your own test results should drive the final call. If Aikido Security earns a place in your stack, write a one-page internal playbook so usage stays consistent as more people join.
Bottom line: Aikido Security is worth a structured trial if your workload matches developer-first AI security from code to runtime and you can measure success on a real task within a week. Use this Aikido Security review as context, use the cards below for scannable facts, and let a hands-on test decide whether it stays in your toolkit.