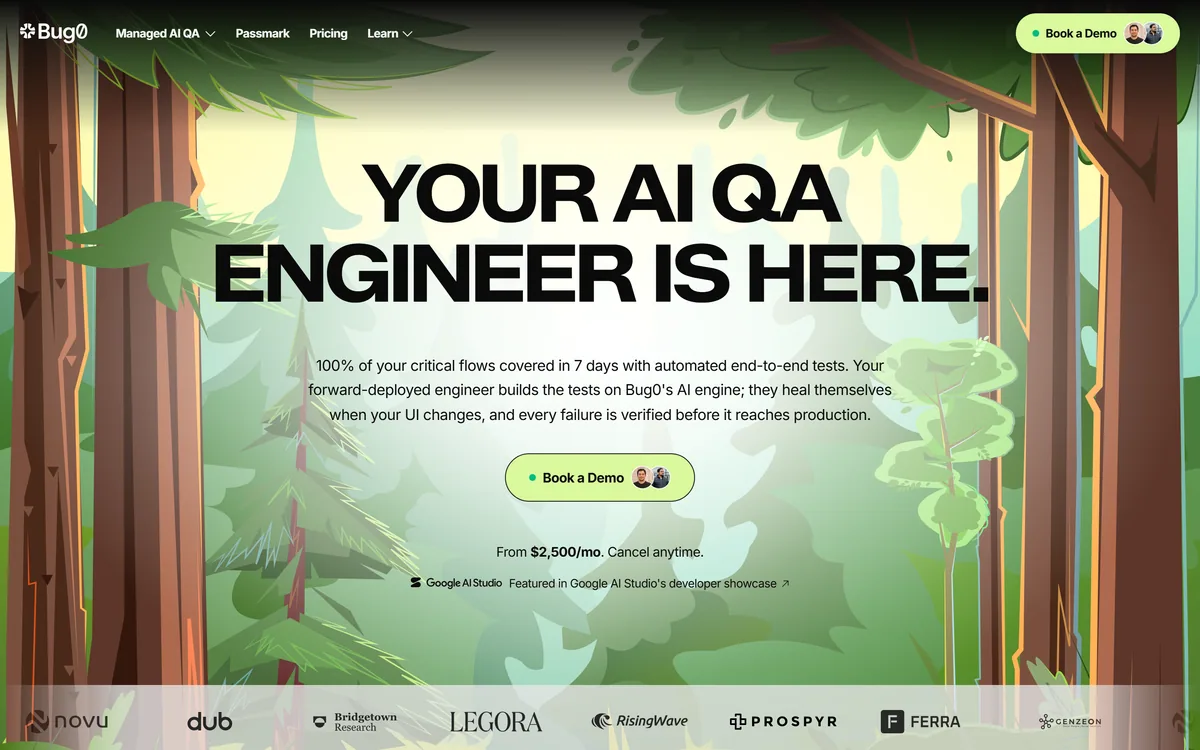
Bug0 is managed AI QA: a forward-deployed engineer builds end-to-end tests on Bug0's engine, covering critical flows in seven days. Tests heal themselves when the UI changes, and every failure is verified before it reaches you. It also publishes Passmark and a substantial testing blog.
Every engineering team knows it should have end-to-end tests, and most have a suite that nobody trusts.
The reason is always the same and it is not technical. Someone wrote the tests during a quiet fortnight, the interface changed, half of them broke, fixing them was nobody's job, and within two months the suite failed on every run and everybody learned to ignore it.
Bug0's answer is organisational rather than clever: it sells the ownership. An engineer builds and maintains the tests on their engine, and every failure is checked before it reaches you — which is precisely the work no team ever staffs.
Bug0: A QA Engineer You Rent
Managed, not self-serve — a forward-deployed engineer builds the tests on Bug0's AI engine rather than handing you a tool.
100% of critical flows covered in seven days, which is the stated commitment.
Tests heal themselves when the UI changes, which is the failure mode that kills every end-to-end suite.
Every failure is verified before it reaches production, so the suite does not cry wolf.
Featured in Google AI Studio's developer showcase, with a substantial technical blog on Playwright and testing practice.
Bug0's homepage, captured 9 September 2026, showing the managed QA positioning and the seven-day coverage claim.
What Does A Forward-Deployed Engineer Change?
Bug0 states that your forward-deployed engineer builds the tests on Bug0's AI engine, which is a managed service rather than a self-serve product, and that distinction is the whole proposition.
The problem with self-serve testing tools is not that they generate bad tests. It is that generating tests was never the bottleneck — maintaining them was, and a tool that produces a hundred tests has produced a hundred things that will break when the interface changes.
Selling an engineer alongside the engine puts the maintenance somewhere it will actually happen. That is expensive, honest, and it is the difference between a suite that exists in six months and one that does not.
Forward-deployed is a specific term worth understanding: an engineer from the vendor working inside your context, on your codebase and your flows, rather than a support ticket queue. They learn what your critical paths are, which is knowledge no tool acquires by itself.
The trade is dependency. A suite built and maintained by someone else is a suite you do not fully own, and the questions to settle before signing are whether the tests are portable, whether they run in your CI, and what you are left holding if you stop paying.
The self-serve version of this is a different bet. A platform like Functionize hands you the automation and leaves the ownership question exactly where it already was.
Generating tests was never the bottleneck. Maintaining them was — and a tool that produces a hundred tests has produced a hundred things that will break.
Self-Healing Tests And Why UI Changes Break Suites
Bug0 states that tests heal themselves when the UI changes, and understanding why they otherwise break explains why this matters more than it sounds.
An end-to-end test identifies elements on a page — click this button, type in that field — and it identifies them by something: a CSS selector, a test ID, a position, a piece of text. Change any of those and the test cannot find what it needs.
That happens constantly, and almost never because anyone broke anything. A designer renames a class, a developer restructures a component, a button moves inside a container — the application works perfectly and forty tests fail.
Those failures are the reason suites get abandoned. A test that fails because the product is broken is valuable; a test that fails because a class name changed is noise, and once the ratio tips toward noise, everyone stops reading the results.
Self-healing means the test re-identifies the element rather than failing. The honest limit is that it must guess which element you meant, and a guess is occasionally wrong in the most dangerous way possible — a test that passes while checking the wrong thing.
Verified Failures Beat Flaky Alerts
Bug0 states that every failure is verified before it reaches production, and this is the second decision that separates it from a tool.
Flakiness is the quiet killer of test suites. A test that fails intermittently for reasons unrelated to the code — a slow network, a timing race, a third-party service having a moment — trains a team to assume failures are noise.
That training is permanent and expensive. Once a team believes the suite cries wolf, a real failure gets the same shrug as a flaky one, and the suite is now worse than useless because it provides false confidence rather than none.
Verifying a failure before surfacing it inverts that. If a failure reaches you, someone or something has already confirmed it is real, which means the correct response to a Bug0 alert is to look — and a team that looks every time is a team the suite is actually protecting.
This is also where a managed service has an unfair advantage over a product. Verification requires judgement and time that a customer's engineers do not have, and selling that labour rather than expecting the customer to supply it is the difference between the model working and not.
The same trust dynamic governs static analysis. Codacy is only useful while developers still read its findings, which is why alert quality matters more than alert coverage.
Establish who owns the tests and whether they are portable before signing anything.
Confirm the suite runs in your own CI rather than only in the vendor's.
Define what a critical flow is yourself — that list is the whole scope.
Watch for self-healing tests that pass while checking the wrong element.
Judge after a quarter on real bugs caught before release, not on tests written.
Getting Critical Flows Covered In A Week
The seven-day claim is a coverage commitment, and understanding what it covers matters more than the timeline.
Critical flows are the paths where a failure costs money: signup, login, checkout, the core action your product exists for.
Write your own list of critical flows before the engagement, because that list defines everything that follows.
Include the paths that are hard to test rather than only the easy ones — payment, third-party integrations, permission boundaries.
Confirm the tests run against your staging environment with realistic data, not a fixture that never changes.
Break something deliberately in week two and check that the suite catches it before anyone tells you.
Review a self-healed test after a UI change, and verify it is still checking the same thing.
Measure after a quarter on bugs caught before release, since that is the only outcome the service is for.
The Blog Is Part Of The Evidence
Bug0 publishes a substantial technical blog — Playwright release analysis, smoke testing, UAT process, spec-driven development, Postman alternatives, Stripe test card references — with named authors and dates.
That is worth mentioning in an evaluation rather than dismissing as marketing. Writing accurately about Playwright internals, testing methodology and payment test scenarios requires the knowledge the service is selling, and it is difficult to fake at length.
It is a form of evidence available to you before any sales conversation. Read two posts in your own area of expertise and judge whether the people writing them know what they are talking about — that tells you more about a managed service than any case study.
The named authors matter for the same reason. A blog written by identifiable engineers rather than a content team is a signal about who works there, and in a service business the people are the product.
The listing is also open about pricing in a way most enterprise services are not, stating a monthly starting figure with cancellation any time. That transparency is unusual for a managed engagement and worth crediting.
Testing before release and monitoring after it are different disciplines — Sentry Seer catches what reached production, which is the failure this service exists to prevent.
Key features of Bug0
A forward-deployed engineer building tests on Bug0's AI engine
Automated end-to-end tests covering critical user flows
Coverage of 100% of critical flows within seven days, as stated
Self-healing tests that survive UI changes
Verification of every failure before it is surfaced
Passmark as a separate product alongside the managed service
A technical blog with named authors on testing practice
Pros & cons
Pros
7
Sells ownership of test maintenance, which is why suites actually rot
A forward-deployed engineer learns your critical flows in a way no tool does
Verified failures prevent the flakiness that trains teams to ignore alerts
Self-healing addresses the class-rename problem that breaks suites weekly
A published starting price with cancel-anytime terms, unusual for a managed service
The technical blog is checkable evidence of expertise before any sales call
Named authors rather than an anonymous content team
Cons
6
A suite someone else maintains is a suite you do not fully own
Portability and what you retain after an engagement are unstated
Self-healing can pass while checking the wrong element, which is the dangerous failure
No customers are named, so there is no external reference
Passmark is listed without explanation
The operating company and its location are not published
Best For
Teams with an abandoned end-to-end suite nobody trusts
Products whose interface changes often enough to break selectors weekly
Engineering groups with no QA function and no appetite to build one
Organisations where flaky alerts have already destroyed trust in testing
Buyers who prefer an outcome to a tool that generates more work
Bug0 Against Other Testing Tools
Quality tooling divides by what it inspects and whether anyone is paid to own the result.
A forward-deployed engineer builds tests on Bug0's AI engine
Coverage commitment
100% of critical flows covered in seven days
Test type
Automated end-to-end tests
Maintenance
Tests heal themselves when the UI changes
Alerting
Every failure verified before it reaches production
Other product
Passmark
Pricing transparency
A monthly starting figure is stated on the site, with cancellation any time
Recognition
Featured in Google AI Studio's developer showcase
Content
A technical blog with named authors covering Playwright, smoke testing, UAT, spec-driven development, Postman alternatives and Stripe test cards
Site sections
Managed AI QA, Passmark, Pricing, Learn, Book a Demo
Should You Outsource QA To Bug0?
Buy the coverage when
You have an end-to-end suite nobody trusts and nobody maintains.
Nobody on the team wants to own test maintenance, which is why it rotted.
Your interface changes often enough that selectors break weekly.
Flaky alerts have already trained your team to ignore failures.
You would rather buy an outcome than a tool that produces work.
Write your own tests when
You have a QA function that already owns and maintains a working suite.
Your tests must be fully portable and vendor-independent by policy.
Your product has no stable critical flows yet, which makes coverage premature.
You need static analysis or production error monitoring, which are different jobs.
You cannot define what your critical flows are, since that list is the entire scope.
Bug0: Reading The Service Description
Last checked . Read from bug0.com in a browser session, with the screenshot above captured alongside.
Positioned as managed AI QA, described on the site as your AI QA engineer
Coverage commitment stated as 100% of critical flows covered in seven days with automated end-to-end tests
Forward-deployed engineer model confirmed, building tests on Bug0's AI engine
Self-healing tests confirmed as the stated behaviour when the UI changes
Every failure stated as verified before it reaches production
A monthly starting price and cancel-anytime terms displayed on the site
Featured in Google AI Studio's developer showcase, stated on the site
Passmark listed as a separate product in the navigation
A technical blog confirmed with named authors and dates, covering Playwright 1.62, smoke testing, spec-driven development, UAT, Postman alternatives and Stripe test cards
Site navigation confirmed for Managed AI QA, Passmark, Pricing, Learn and Book a Demo
What we could not confirm: the operating company's legal name or location; what Passmark is, beyond its presence in the navigation; whether tests are portable, and what you retain if the engagement ends; which CI systems are supported; how self-healing decides which element was meant; whether the seven-day commitment carries any guarantee; how many customers the service has, since none are named; and which underlying models the engine uses. We did not use the service, so nothing here reflects tested coverage.
Editor's Verdict
4.2/5
Bug0's model is more interesting than its technology. Most AI testing tools are self-serve products that generate tests you then maintain, which means the maintenance problem simply moves. Bug0 sells a managed service — a forward-deployed engineer builds the tests on their engine — which is the honest answer to why test suites rot: nobody owns them. Verifying every failure before it reaches you is the second good decision, because a flaky suite that cries wolf gets ignored within a fortnight and then the whole investment is dead. It scores highly for solving the organisational problem rather than only the technical one. AInexfinder Editor Score: 4.2/5.
Bug0 pricing
AInexfinder does not list plan prices or billing details. For current pricing, plans, and trials, visit the official Bug0 website.
Vendor pricing, credits, and billing policies change over time. Always confirm on the official site before you buy.
Frequently asked questions
What is Bug0?
Bug0 is a managed AI QA service. A forward-deployed engineer builds automated end-to-end tests on Bug0's AI engine, with a stated commitment of covering 100% of critical flows in seven days. Tests heal themselves when the UI changes, and every failure is verified before it reaches you.
Why does a managed service beat a testing tool?
Because generating tests was never the bottleneck — maintaining them was. A tool that produces a hundred tests has produced a hundred things that will break when the interface changes, and fixing them is nobody's job. Selling the ownership puts the maintenance somewhere it will actually happen.
What is a forward-deployed engineer?
A vendor engineer working inside your context, on your codebase and your flows, rather than through a support ticket queue. The practical difference is that they learn what your critical paths actually are — knowledge no tool acquires by itself and no generic test suite encodes.
Why do end-to-end test suites break so often?
Because tests identify elements by selectors, test IDs, positions or text, and all of those change constantly for reasons unrelated to correctness. A designer renames a class, a developer restructures a component, the application works perfectly, and forty tests fail. That noise is what makes teams abandon suites.
Is self-healing risky?
It has one dangerous failure mode. Healing means the test re-identifies the element it thinks you meant, and a wrong guess produces a test that passes while checking the wrong thing — which is worse than a failing test, because it provides false confidence. Review self-healed tests after any significant UI change.
Why does verifying failures matter?
Because flakiness is what kills suites. A test that fails intermittently for unrelated reasons trains a team to assume failures are noise, and that training is permanent — a real failure then gets the same shrug. If every alert has been confirmed real, the correct response is always to look.
What do I own if I stop paying?
Not stated on the pages we read, and it is the most important question to settle before signing. Whether the tests are portable, whether they run in your own CI, and what you retain after an engagement all determine whether this is a service or a dependency.
How do I define critical flows?
Write the list yourself before the engagement, because it defines everything that follows. Critical flows are the paths where failure costs money — signup, login, checkout, the core action your product exists for. Include the hard ones: payment, third-party integrations, permission boundaries.
Is the blog worth reading before buying?
Yes, and it is genuine evidence rather than marketing. Writing accurately about Playwright internals, UAT methodology and Stripe test scenarios requires the knowledge the service sells, and it is hard to fake at length. Read two posts in your own area of expertise and judge whether the authors know their subject.
How should I measure whether it worked?
Real bugs caught before release, after a quarter. Not tests written, not coverage percentage, not alerts raised. The service exists to stop broken things reaching production, so break something deliberately in week two and check the suite catches it before anyone tells you.
Daniel reviews AI tools the slow way — by actually using them on real projects. His reviews cover what works, what breaks, and who each tool is genuinely a good fit for.
Daniel and the AInexfinder editorial team research Bug0 using public product information, listing evidence, and (when available) hands-on checks. Scores reflect listing completeness and transparency — not paid placement.
Listings may include affiliate or sponsored placements, which are labeled when present. Editorial scores and cons are not sold. See our affiliate disclosure and review methodology.
Momentic is an agentic end-to-end testing platform where AI writes tests as plain-English YAML, runs them across web, iOS and Android, and self-heals them when the UI changes, with an autonomous bug-bashing agent, an MCP server and CI integration.
Helicone is open-source LLM observability and an AI gateway. It logs and analyses requests across OpenAI, Anthropic, Gemini, Mistral, Groq, Together and OpenRouter, with sessions, user-level tracking, a query language, prompt management, datasets, a playground, rate limits and alerts.
Langfuse is an open-source LLM engineering platform covering tracing, evaluation, prompt management, experiments and human annotation. Every product feature is MIT licensed, with self-hosting via Docker Compose, Kubernetes or Terraform alongside a managed cloud in US and EU regions.
Functionize is an AI-native test automation platform for enterprise web applications. Its Studio product uses autonomous agents to create and run end-to-end UI tests, with self-healing element resolution built on custom models rather than brittle selectors, across Salesforce, ServiceNow, Workday, SAP and bespoke apps.
GitHub Copilot is an AI coding assistant that spans completion, chat, agent mode, automated code review, and a cloud agent that opens pull requests, working across VS Code, Visual Studio, JetBrains, Xcode, Neovim, Eclipse, the CLI, and github.com.
Replit AI turns a written description into a working application — the Agent writes the code, and Replit supplies the database, authentication, hosting, and monitoring, so a prototype goes live without a local setup or a deployment pipeline.